OSSEC HIDS

OSSEC HIDS 4.3.0

Host-based intrusion detection for Windows

OSSEC HIDS is an open-source host-based intrusion detection system for monitoring Windows computers across a network. Its agent reports activity to a separately configured OSSEC server, which manages policies. The agent can monitor event logs in real time, check system folders and registry changes, verify file integrity, and detect signs of rootkits. IIS scanning and log monitoring are available for relevant servers. Setup requires the server address, an authentication key and manual editing of a configuration file.

OSSEC HIDS 4.3.0 details

Author:
License: Open Source
Price: FREE
Released:
File size: 3.20 MB
Downloads: 62
Keywords: host intrusion detection, rootkit detection, intrusion, log monitoring, download OSSEC HIDS, ossec hids, file integrity monitoring, log analyzer, windows security monitoring, analyzer, intrusion detector, OSSEC HIDS, OSSEC HIDS free download, rootkit, detector
Author URL: https://www.trendmicro.com/
OSSEC HIDS screenshot
OSSEC HIDSOtherWindows Server 2025, Windows 11, Windows Server 2022, Windows Server 2019, Windows Server 2016, Windows 10 32/64 bit, Windows Server 2012 R2, Windows Server 2012, Windows 2008 R2, Windows 2008 32/64 bit, Windows 2003, Windows 8 32/64 bit, Windows 7 32/64

User Rating: 0 (0 votes)

OSSEC HIDS for Windows 10 - Full description

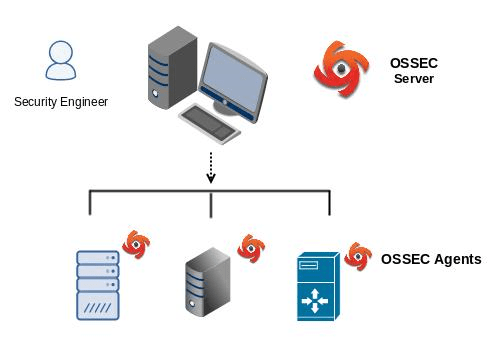
OSSEC HIDS is an open-source host-based intrusion detection system for administrators who need to monitor the security state of computers across a network. Its Windows agent collects host activity and reports it to an OSSEC server, where centrally managed policies can be applied and alerts reviewed. The agent is intended to work as part of this client-server setup rather than as a standalone security dashboard.

The agent can monitor Windows event logs in real time, helping administrators spot activity that may warrant investigation. File integrity checking watches selected system folders for changes, which can reveal unexpected modifications to important files. Registry monitoring provides another view of changes to Windows configuration, while rootkit detection checks for signs of software designed to hide malicious activity. IIS scanning and log monitoring can also be selected during installation when those components are relevant to a server's role.

After the OSSEC server has been prepared, the agent is connected by entering the server address and an authentication key. The agent then sends monitoring data to that server, which manages policies for connected machines. Configuration is handled by editing a text file, allowing administrators to adjust the agent's parameters directly. This approach offers control over deployment but requires familiarity with the settings and the OSSEC environment; routine installation is only one step in a broader security setup.

OSSEC HIDS is suited to system administrators and security teams responsible for monitoring servers or other networked Windows computers. It can help with change monitoring, event-log review, rootkit checks and verifying that machines follow intended policies. The agent's collected information can support investigations and ongoing oversight, but effective use depends on a correctly configured server and an administrator who can interpret alerts and maintain the configuration.

The software is open source and is available for Windows client and server systems, including Windows 10 and 11 and a range of Windows Server releases. This download is the Windows agent component; a separate OSSEC server must be set up to receive and manage its reports. Administrators should select the monitoring components needed for each machine and configure the agent's text file to suit their deployment.

OSSEC HIDS for Windows 10 - Post your review