MailEnable Log Analysis Utility
MailEnable Log Analysis Utility is a small diagnostic tool for administrators and support staff working with MailEnable mail server log files. It scans log files for errors ...

Syslog Watcher collects, parses, stores and exports syslog messages from network devices, servers and software. Its service receives logs over UDP or TCP/IP on IPv4 and IPv6 networks, and can be monitored remotely. The parser supports RFC 3164 and identifies message sources and types. Export selected entries to ODBC databases or XML, CSV and TXT files, with options to split output.
| Author: | EZ5 Systems Ltd |
| License: | Demo |
| Price: | $245.00 |
| Released: | Oct 22, 2026 |
| File size: | 17.10 MB |
| Downloads: | 1039 |
| Keywords: | download Syslog Watcher, Syslog Server, remote appliance monitoring, export syslog logs, network monitoring, Syslog Monitor, syslog parser, Monitor, syslog monitoring, Syslog Watcher, Syslog, syslog server, remote device monitoring, Network, Server, network log analysis, Syslog Protocol, log expor, Syslog Watcher free download, log analysis |
| Author URL: | https://ezfive.com/eventlog-inspector/ |


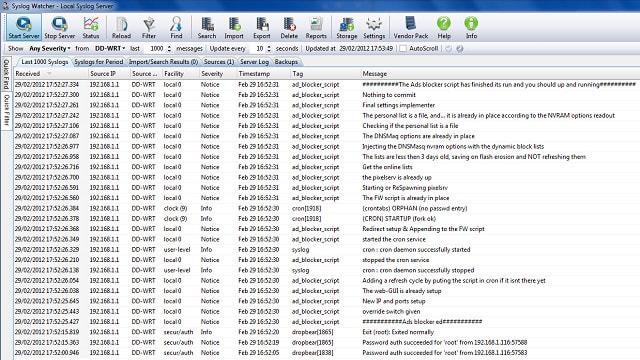
Syslog Watcher is a syslog server and log analysis tool for administrators who need to collect messages from network equipment, servers, computers and software. It receives events sent by devices such as firewalls, switches, routers and modems, then parses and stores them for review. The program can be used as a network monitor or as a local auditing utility, with a background service for ongoing collection.
The service accepts syslog traffic over UDP or TCP/IP across IPv4 and IPv6 networks. It can receive messages from individual appliances, dedicated forwarders and other applications that send logs using the syslog protocol. Administrators can connect to the service remotely to monitor network appliances, or run it locally to capture events from nearby systems. This makes it useful for gathering logs from equipment distributed across a network without relying on each device's own interface for review.
Incoming messages are parsed according to their syslog structure. The parser examines each entry to identify its source and message type, helping the application handle differences between senders while supporting the RFC 3164 format. Parsed messages are kept in storage designed for syslog data, so administrators can retain earlier entries and examine them alongside current activity. This provides a central place to investigate device events and review records from multiple sources.
For reporting or further analysis, Syslog Watcher exports messages to ODBC-compliant databases and local files. File formats include XML, CSV and plain text. Users can choose specific entries for export and split output files according to their requirements, which helps when preparing selected records for another tool or managing large collections of logs. The combination of continuous collection, parsing, storage and export suits routine network monitoring as well as troubleshooting and audit work.
Syslog Watcher is commercial software offered as a demo. It supports Windows desktop and server editions, including Windows 10 and 11 and several Windows Server releases. Its network protocols and remote monitoring capabilities make it intended primarily for administrators managing syslog-enabled devices and systems.