WinDump
... For standard packet capture, WinDump relies on the WinPcap library and drivers, which must be available separately; capture access can also depend on interface and ...

WinPcap provides a Windows driver and library for capturing and transmitting network packets at the link layer, outside the normal protocol stack. Kernel-level filtering, buffering and statistics help applications process traffic efficiently. Network tools use it for protocol analysis, monitoring, security testing and diagnostics, while developers can build on its libpcap-compatible API.
| Author: | CACE Technologies Inc. |
| License: | Freeware |
| Price: | FREE |
| Released: | Mar 11, 2013 |
| File size: | 922 kB |
| Downloads: | 2688 |
| Keywords: | libpcap for windows, network traffic analysis, library, link layer access, network packet capture, software analysis tool, CACE Technologies Inc., protocol stack, network access, layer, Packet Library, packet, winpcap download, Windows 10 compatibility, WinPcap, x64 architecture, packet capture library |
| Author URL: | http://www.cacetech.com/ |



WinPcap is a Windows packet-capture driver and programming library for applications that need low-level access to network traffic. It is used by network administrators, security analysts and developers building tools for protocol inspection, monitoring, testing or diagnostics. Rather than relying on the normal protocol stack, compatible software can capture and transmit packets at the link layer through WinPcap.
The package combines a driver, which provides low-level network access, with a library based on the familiar libpcap API. This lets supported applications work with network interfaces using a common programming interface. A kernel-level filtering engine can select packets before they reach the application, reducing the amount of traffic that needs to be processed. Buffering and other capture optimizations support efficient collection, while kernel-level statistics provide traffic measurements without requiring every packet to be handled individually.
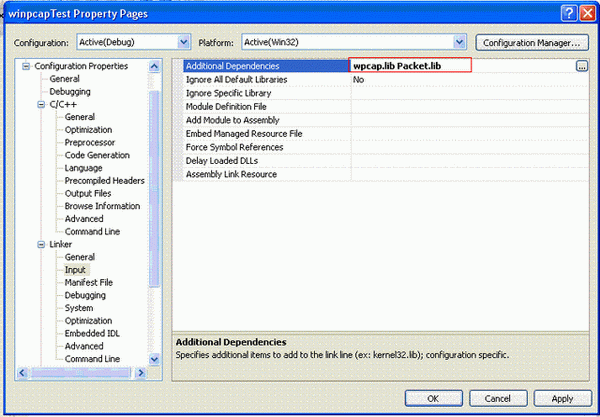
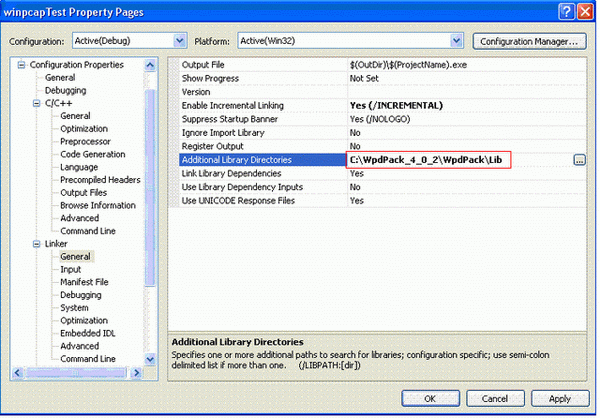
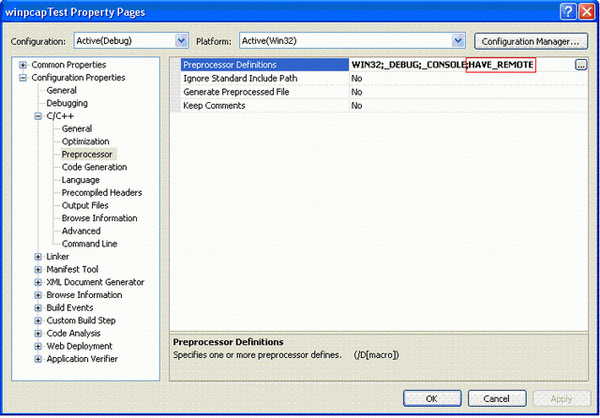
WinPcap also supports packet transmission and remote packet capture. Developers can use its programming components, documentation, libraries, include files and sample programs as a starting point for Windows network software. For users, installing the driver makes packet capture available to compatible utilities. Tools such as Wireshark, Nmap, Snort, ntop and WinDump have used WinPcap for tasks including protocol analysis, network discovery, intrusion detection and traffic inspection.
Typical work includes examining packet contents to troubleshoot connectivity, monitoring network activity, testing network services and collecting traffic for security analysis. WinDump, a Windows implementation of tcpdump, can watch traffic and save selected packets to disk according to filtering rules. WinPcap itself is an underlying component rather than a graphical analyzer: users generally work through an application that relies on its capture and filtering functions, while developers integrate the library into their own tools.
WinPcap is freeware and is intended for Windows systems. The supplied compatibility information includes Windows 2000, Windows Server 2003, Windows XP, Windows Vista, Windows 7, Windows 8 and Windows 10, including some 64-bit editions. Its low-level driver role means it must be installed for applications that depend on it to capture traffic. The developer package is aimed at programmers who need the headers, libraries and examples to build compatible software.